
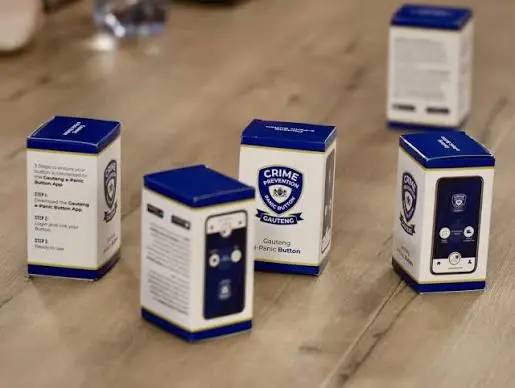
The Information Regulator is to engage the Gauteng department of e-Government over a reported security breach involving the province’s e-Panic Button, after confirming that it has not received a notification of the incident from the department.
Regulator spokesperson Nomzamo Zondi told the Mail & Guardian: “Given the severity and sensitivity around the alleged security compromise, we will engage with the responsible party (eGovernment Department) to establish details around the alleged breach and urge them to adhere to the provisions of Popia [Protection of Personal Information Act] when a body experiences a security compromise.”
The regulator was also empowered to issue an information notice to obtain details it needed to determine how to proceed, she said.
The development follows a recent investigation by GroundUp, which found that the database behind Gauteng’s e-Panic Button app had been left unsecured, exposing crime reports and personal information linked to people who had used the platform.
GroundUp reported that the exposed information included names, phone numbers, email addresses, vehicle registration numbers, GPS coordinates and movement histories, as well as the contents of crime reports and photographs.
Some reports concerned domestic violence and assault. The investigation also found that more than 5 000 crime report images were exposed to the internet.
GroundUp said it alerted the Gauteng government and Evolve Value Added Services, the company involved in the development of the platform, on 21 September. Evolve responded and subsequently fixed the reported vulnerabilities.
The Democratic Alliance subsequently said it would report the matter to the Information Regulator and called for the Gauteng department of e-Government to appear before the legislature’s portfolio committee.
DA Gauteng spokesperson on e-Government Michael Waters said the party wanted answers about how long the information had been exposed, whether it had been accessed by unauthorised people and whether access logs had been independently examined.
Waters said residents reporting domestic violence, assault and other serious crimes needed to be able to trust that the information they provided to the government would be protected. He said someone reporting an alleged abuser could potentially have had their identity, location, movements and crime report exposed.

The DA also questioned why the department had not informed the portfolio committee about the incident.
On Tuesday, however, the Gauteng government issued its first public response to the reports, describing the incident as an “attempted security breach”, which had been “swiftly identified and addressed”.
The department said it had established that “no citizens’ personal information was compromised as a result of the incident”.
It said the incident involved a “highly specialised organisation with advanced cybersecurity expertise and capabilities in vulnerability identification and security testing”.
MEC for e-Government, Research and Development Bonginkosi Dhlamini said the department’s technical teams had acted to address the identified vulnerabilities and strengthen the platform’s security controls. The department said it had also requested additional testing and verification.
The Information Regulator said the department’s obligations under section 22 of Popia would depend on the circumstances established around the incident.
Zondi said the section requires a responsible party to notify the regulator and affected data subjects “as soon as there are reasonable grounds to believe that personal information has been accessed or acquired by an unauthorised person”.
Asked whether the regulator had opened an investigation or compliance assessment into the reported breach, Zondi said it had recently conducted a Popia compliance assessment of the Gauteng e-Government department but that the outcome had not yet been finalised.
“With this development, we will look into the matter to determine if there is a need to obtain further information from the responsible party and take the necessary steps and determine the appropriate regulatory action in accordance with our mandate and the provisions of Popia,” she said.
The regulator also confirmed that it was concerned about the broader increase in security compromises in South Africa. “On this matter, we will be contacting the department,” Zondi said.
Zondi said section 22 requires affected data subjects to be notified when there were reasonable grounds to believe that their personal information had been accessed or acquired by an unauthorised person.
The Gauteng government has said that no citizens’ personal information was compromised and has urged residents to continue using the e-Panic Button. The province said the platform had 288 307 active users, had recorded 59 394 reported crimes and had an average response time of 15 minutes and 57 seconds.
The M&G asked the Gauteng department of e-Government when it first became aware of the reported exposure, whether the Information Regulator had been notified, whether affected users would be informed and whether access logs had been examined to establish whether unauthorised people had accessed the information.
The department had not responded by the time of publication.